nordbank-verify.com
Registered 3 days ago. Copies ShopNova's login form and asks for a password.
What do I do · nothing — this finding is closed
Closed by an analyst · · a legitimate site.
Notes · for you and the next analyst — kept with the finding, never edited, also in Activity
No notes yet.
Explain Finding — why it was flagged · every signal, its points and the evidence behind it
| Signal | Group | Points | Evidence |
|---|---|---|---|
| asks for a password credential_form | Behaviour | +14 | page contains a password field |
| cloned login form login_dom_similarity | Visual | +12 | login form markup is 100% identical to the brand's |
| registered < 7 days ago age_lt_7d | Freshness | +10 | domain registered 3 day(s) ago |
| registered < 30 days ago age_lt_30d | Freshness | +6 | domain registered 3 days ago |
| urgent lure wording lure_language | Behaviour | +6 | lure phrases: verify your account; unusual activity; your account will be |
How the score adds up
⚙ deterministic · versioned Raw 42 of 150 → normalised to 28 / 100.
Thresholds: Medium 25 · High 50 · Critical 75 · scoring v2-c213b21d
open the arithmetic ↗ — this site's section of the scan trace
Group caps ? · stop correlated evidence from double counting
Confidence ? · 65%
| Breadth (3 independent groups) | +50 |
| Hard confirmers | +0 |
| Evidence completeness | +15 |
| Provider agreement | +0 |
| Unavailable evidence | 0 |
| Single weak signal | 0 |
Suspect vs. official similarity 50%
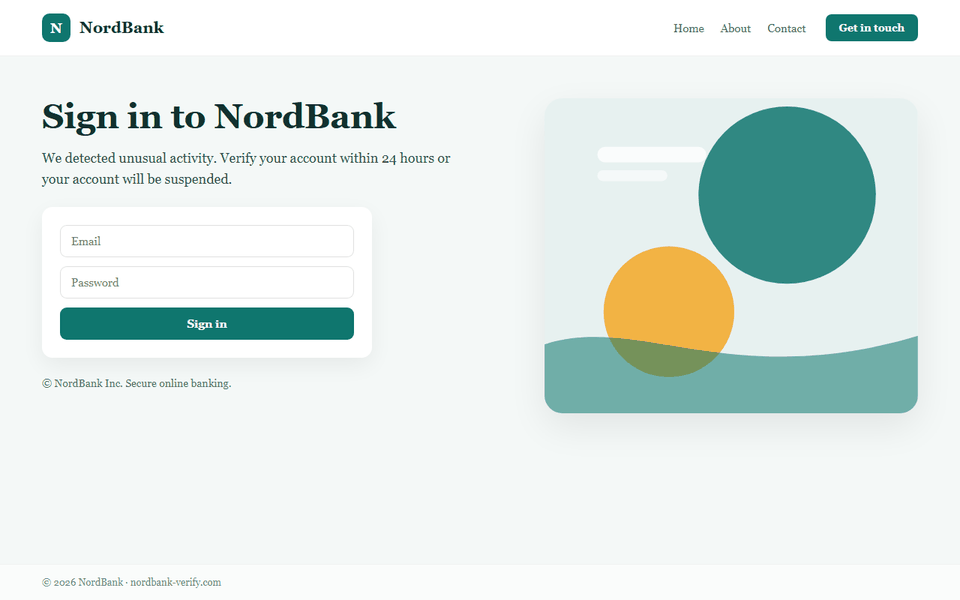
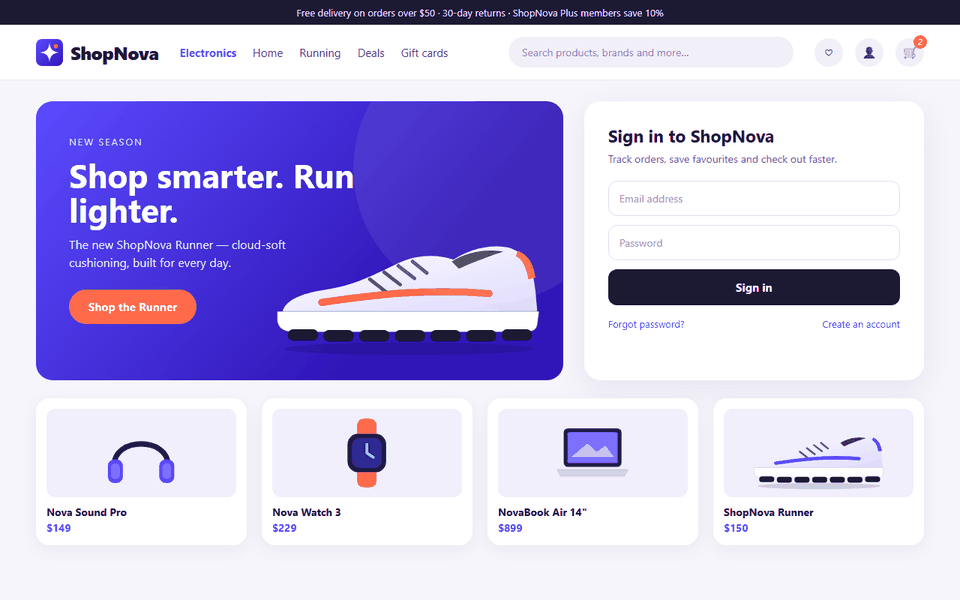
Cloaking multi-probe ? ⚙ Tier 3/4 multi-probe
| Probe | Profile | Login form | Diverged | Note |
|---|---|---|---|---|
| bot | bot | yes | same | |
| param | datacenter | yes | same | |
| referer | referer | yes | same | |
| residential | residential | yes | same |
Fetched several ways — a crawler user-agent, a victim-style link (?email=), a Google referer, a phone (when chosen in Settings → Proxy) and a real home or phone-network IP (Tier 4). Residential (Tier 4): used. Residential IPs are used to look, never to interact.
Not investigated yet
VirusTotal's verdict from 70+ security vendors, every engine's result and category, and the AbuseIPDB abuse score of each server hosting the site. Google Safe Browsing and URLhaus are already in the header — the scan checks them.
Press Run investigation above: one pass over the APIs, cached for 24 hours.
Look it up elsewhere
Each link opens the external service's own page for this site — nothing is sent from here beyond the name in the URL.
Not investigated yet
RDAP registration and the registrar's abuse contact, the full WHOIS history (every owner, transfer and privacy change — and owner details that were hidden later), DNS records and the HTTPS certificate.
Press Run investigation above: one pass over the APIs, cached for 24 hours.
Not investigated yet
Every server hosting the site with its AbuseIPDB score and every other site on it, the urlscan.io scan with pages that share the same kit, passive DNS, subdomains, historical certificates and malware that contacted the domain.
Press Run investigation above: one pass over the APIs, cached for 24 hours.
Observation timeline
- 2026-10-12 06:41:58 · HTTP 200 · state new · datacenter · content changed · ac90cb11542b · screenshot
first seen 2026-10-12 06:41 · scans 1 · next — · candidate state dismissed · WHOIS history →
Score history
| When | Score | Severity | Confidence | Version |
|---|---|---|---|---|
| 2026-10-12 06:41:58 current | 28 | medium | 65% | v2-c213b21d |
Evidence · chain of custody ? ⚙ immutable · DB-enforced
Append-only by the database: UPDATE and DELETE are rejected by triggers, even for an admin. Every artifact is stored under its own SHA-256, so the hash is literally the file name — any tampering is visible. Role: primary = proves a signal · supporting = corroborates · contradicting = argues the site is legitimate · context = background.
| Observed (UTC) | Type | Role | Source | SHA-256 | Details | |
|---|---|---|---|---|---|---|
| 2026-10-12 06:41:58 | http · residential view | supporting | mock:playwright | ac90cb11542bf02c | probe: residential status: 200 content_sha256: ac90cb11542bf02c359cdb9ea6c… +3 | |
| 2026-10-12 06:41:58 | http · referer view | supporting | mock:playwright | ac90cb11542bf02c | probe: referer status: 200 content_sha256: ac90cb11542bf02c359cdb9ea6c… +3 | |
| 2026-10-12 06:41:58 | http · param view | supporting | mock:playwright | ac90cb11542bf02c | probe: param status: 200 content_sha256: ac90cb11542bf02c359cdb9ea6c… +3 | |
| 2026-10-12 06:41:58 | http · bot view | supporting | mock:playwright | ac90cb11542bf02c | probe: bot status: 200 content_sha256: ac90cb11542bf02c359cdb9ea6c… +3 | |
| 2026-10-12 06:41:58 | reputation | contradicting | mock:safebrowsing | — | status: negative | |
| 2026-10-12 06:41:57 | reputation | context | mock:urlhaus | — | status: unknown | |
| 2026-10-12 06:41:57 | reputation | context | mock:virustotal | — | status: unknown | |
| 2026-10-12 06:41:57 | whois | primary | mock:rdap | — | status: positive | |
| 2026-10-12 06:41:57 | favicon | context | mock:playwright | 0a9e706fde508362 | mmh3: 1455436156 phash: 9ece613199ccc693 | artifact |
| 2026-10-12 06:41:57 | screenshot · datacenter view | primary | mock:playwright | fe77552ec18dab90 | phash: ca5ab5a5a5d2421f dhash: c431493172c11c61 palette: ['#f4f8f7', '#edf3f2', '#fb… | artifact |
| 2026-10-12 06:41:57 | html · datacenter view | primary | mock:playwright | ac90cb11542bf02c | title: NordBank — Sign in forms: 1 parked: False | artifact |
| 2026-10-12 06:41:57 | http | supporting | mock:playwright | ac90cb11542bf02c | status: 200 final_url: https://nordbank-verify.com/ content_type: text/html; charset=utf-8 |
show all 13 evidence rows from 1 scan(s)
| 2026-10-12 06:41:57 | dns | supporting | mock:local_dns | — | status: positive |
Advisory opinions · shown for context, never part of the score ⚙ AI advisory · JSON schema
AI · mock:openai phishing impersonating NordBank · 85% — credential form; lure language; page presents itself as NordBank
classifier · ml-5edcdd68-18 P(phishing) = 42% (cross-validated accuracy 96%)