cooinpilot.io
Is one or two typos away from CoinPilot, copies CoinPilot's favicon, homepage and login form and asks for a password. It shares infrastructure with phishing BrandWatch already mapped.
 198.51.100.79
registrar Mock Registrar LLC
What do I do · get it taken down
Notes · for you and the next analyst — kept with the finding, never edited, also in Activity
No notes yet.
Explain Finding — why it was flagged · every signal, its points and the evidence behind it
| Signal | Group | Points | Evidence |
|---|---|---|---|
| forwards with an affiliate id affiliate_redirect | Behaviour | +25 | the visit ends on the brand's own site after a link with atid=51803: the commission goes to the owner of that id |
| identical favicon favicon_exact | Visual | +22 | favicon mmh3 1130316202 equals the brand's favicon hash |
| forwards through another host redirect_via_third_party | Infrastructure | +20 | the visit goes through go-linkz.click on its way to the brand's own site: the destination can be changed at any time |
| looks like the real site screenshot_similarity_ge_90 | Visual | +18 | homepage screenshot is 100% similar to the brand's (pHash) |
| shares a server with phishing cohosted_with_known_phish | Infrastructure | +15 | shares server 198.51.100.79 with known phishing of this brand |
| linked to a mapped attacker linked_to_known_campaign | Infrastructure | +15 | shares infrastructure with an investigated campaign of this brand |
| asks for a password credential_form | Behaviour | +14 | page contains a password field |
| shares a certificate with phishing cert_shared_with_phish | Infrastructure | +12 | TLS certificate fingerprint also used by known phishing |
show all 12 signals, bonuses and false-positive checks
| cloned login form login_dom_similarity | Visual | +12 | login form markup is 100% identical to the brand's |
| 1–2 typos away levenshtein_le_2 | Identity | +8 | 'cooinpilot' is 1 edit(s) from 'coinpilot' |
| brand words in the text brand_keywords_in_content | Behaviour | +6 | brand terms in content: automated, autopilot, bots, coinpilot, crypto |
| same colours palette_match | Visual | +5 | 100% of the page's dominant colours match the brand's |
| combination bonus | cluster | +15 | favicon_exact + credential_form + levenshtein_le_2 |
| redirects to the official site redirects_to_official | false-positive check | -60 | lowers the score: a sign the site may be legitimate |
How the score adds up
⚙ deterministic · versioned Raw 43 of 150 → normalised to 75 / 100 · severity raised to critical by the rule “pixel-perfect clone with a login form (favicon + screenshot + password form)”.
Thresholds: Medium 25 · High 50 · Critical 75 · scoring v7-f1ba3ebf
Other rules that fired: a login page tied to an already-mapped attacker (≥ high); affiliate redirect verdict (≥ medium); redirect service verdict (≥ high)
open the arithmetic ↗ — this site's section of the scan trace
Group caps ? · stop correlated evidence from double counting
Confidence ? · 100%
| Breadth (4 independent groups) | +60 |
| Hard confirmers favicon_exact, linked_to_known_campaign | +30 |
| Evidence completeness | +15 |
| Provider agreement | +0 |
| Unavailable evidence | 0 |
| Single weak signal | 0 |
Suspect vs. official similarity 100%
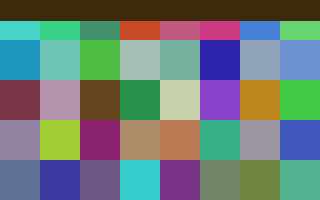
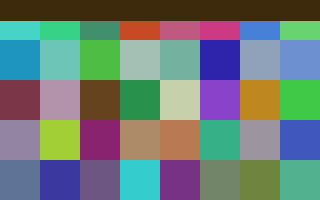
Cloaking multi-probe ? ⚙ Tier 3/4 multi-probe
| Probe | Profile | Login form | Diverged | Note |
|---|---|---|---|---|
| bot | bot | yes | same | |
| param | datacenter | yes | same | |
| referer | referer | yes | same | |
| residential | residential | yes | same |
Fetched several ways — a crawler user-agent, a victim-style link (?email=), a Google referer, a phone (when chosen in Settings → Proxy) and a real home or phone-network IP (Tier 4). Residential (Tier 4): used. Residential IPs are used to look, never to interact.
VirusTotal · security vendors
Server reputation · AbuseIPDB
Categories
JARM
Engines flagged first
| Engine | Category | Result | Method |
|---|---|---|---|
| BitDefender | harmless | clean | blacklist |
| CRDF | harmless | clean | blacklist |
| ESET | harmless | clean | blacklist |
| Fortinet | harmless | clean | blacklist |
| Google Safebrowsing | harmless | clean | blacklist |
| Kaspersky | harmless | clean | blacklist |
| Netcraft | harmless | clean | blacklist |
| OpenPhish | harmless | clean | blacklist |
| Phishtank | harmless | clean | blacklist |
| Quttera | harmless | clean | blacklist |
| Sophos | harmless | clean | blacklist |
| Webroot | harmless | clean | blacklist |
Look it up elsewhere
Each link opens the external service's own page for this site — nothing is sent from here beyond the name in the URL.
Registration data (RDAP)
- Name
- cooinpilot.io
- registration
- 2026-09-01
- Status
- —
- DNSSEC
- —
Registrar & abuse contact
- Registrar
- Mock Registrar LLC
- Abuse email
- —
- registrant email
- ops@affnet-mail.example
Nameservers
—Current WHOIS record (VirusTotal)
WHOIS history · every WHOIS snapshot WhoisXML has recorded for cooinpilot.io
Who registered the domain, when, through which registrar, and every change since: transfers, new owners, re-registration after expiry, privacy switched on or off. Phishers often register with their real details and hide them a day later — that first snapshot is a lead.
First registered
Snapshots
Owners seen
Registrars
Owner details now
Same owner e-mail on other domains in this workspace
Found in other domains' WHOIS history and in the WHOIS evidence of your scans — no extra API call. One operator, several kits.
TIMELINE
- 2026-09-01Registered by ops@affnet-mail.examplevia Mock Registrar LLC · first WHOIS snapshot 2026-09-02
SNAPSHOTS · CHANGED FIELDS MARKED
| Seen | Registrar | Registrant | Created · expires |
|---|---|---|---|
| 2026-09-02 | Mock Registrar LLC | ops@affnet-mail.example | 2026-09-01 · 2027-09-01 |
raw WHOIS · 2026-09-02Domain Name: COOINPILOT.IO
Registrar: Mock Registrar LLC
Creation Date: 2026-09-01T00:00:00Z
Updated Date: 2026-09-02T00:00:00Z
Registry Expiry Date: 2027-09-01T00:00:00Z
Registrant Organization:
Registrant Name:
Registrant Email: ops@affnet-mail.example
Name Server: NS1.MOCK-DNS.EXAMPLE
Name Server: NS2.MOCK-DNS.EXAMPLE | |||
Source: WhoisXML WHOIS History API (whois-history.whoisxmlapi.com) · cached 24 h · fetched .
DNS records source: VirusTotal
A records are the servers hosting the site — click one to see everything else hosted there. NS tells you who runs its DNS (Cloudflare nameservers hide the real origin).
| Type | TTL | Value |
|---|---|---|
| A | 300 | 198.51.100.79 |
| AAAA | 300 | 2001:db8::1480 |
| NS | 21600 | ns1.mock-dns.example |
| NS | 21600 | ns2.mock-dns.example |
| MX | 3600 | mail.cooinpilot.io prio 10 |
| SOA | 1800 | ns1.mock-dns.example rname hostmaster.cooinpilot.io · serial 2026100801 |
HTTPS certificate from VirusTotal
- Common name
- cooinpilot.io
- Issuer
- C=US O=Mock Trust Services CN=MT1
- Valid
- 2026-09-20 00:00:00 → 2026-12-19 00:00:0032% of the validity period elapsed
- Alt names (2)
- cooinpilot.io www.cooinpilot.io
- SHA-256
- 35aba6f4ecc4b34d880fd2ef29fb7144f2dbb4ee0c7ef0b697ee8292beb7ec2b · crt.sh ↗
serial, signature, key, TLS and the full certificate
- Subject
- CN=cooinpilot.io
- Serial
- e3e1309e
- Signature
- sha256ECDSA
- Public key
- EC secp256r1
- SHA-1
- f8a29b8dcd94c2d8f28594d703cbfbf0dfa8a664
 198.51.100.79
Abuse reports · AbuseIPDB — what other defenders reported about this server in the last 90 days
SITES HOSTED ON THIS SERVER (passive DNS, each with its own detections)
COMMUNICATING FILES not fetched yet
IP WHOIS record
engine verdicts for this IP (12)
| Engine | Category | Result |
|---|---|---|
| BitDefender | harmless | clean |
| CRDF | harmless | clean |
| ESET | harmless | clean |
| Fortinet | harmless | clean |
| Google Safebrowsing | harmless | clean |
| Kaspersky | harmless | clean |
| Netcraft | harmless | clean |
| OpenPhish | harmless | clean |
| Phishtank | harmless | clean |
| Quttera | harmless | clean |
| Sophos | harmless | clean |
| Webroot | harmless | clean |
urlscan.io scan
 Netherlands
203.0.113.66AS64512 BulletproofHost BV
server nginx
23 requests · 2 domains · 1 IPs · 1 countries
scanned 2026-10-14 09:46
domains contacted by the page (2)
Similar sites 4
Other pages urlscan has seen that share this site's page hash (same kit), its server, or the brand name.
Same page (identical document hash) 4hash:1e6b399a726812c985d8eb08261953b8bee34f6b8292a09a47a290b27df15e45
the same HTML served elsewhere — the same phishing kit
| Seen | Verdict | Domain | Title | |
|---|---|---|---|---|
| 2026-09-16 | — | shopn0va.com |
urlscan ↗ · VT ↗ | shopn0va.com - Sign in |
| 2026-09-15 | — | shopnova-login.com |
urlscan ↗ · VT ↗ | shopnova-login.com - Sign in |
| 2026-09-14 | — | secure-shopnova.com |
urlscan ↗ · VT ↗ | secure-shopnova.com - Sign in |
| 2026-09-08 | — | shopnova.co |
urlscan ↗ · VT ↗ | shopnova.co - Sign in |
Same server 0page.ip:203.0.113.66
other pages scanned on the same IP
noneSame brand name 0page.domain:*coinpilot*
domains containing the brand name
nonePassive DNS replication 1
Every IP this domain has resolved to, with how many engines flag that IP. Click an IP to see the other sites on it.
| Date resolved | Detections (IP) | IP |
|---|---|---|
| 2026-09-27 | 3/ 92 | 198.51.100.79 |
Subdomains 3
| Host | Detections |
|---|---|
| login.cooinpilot.io | 2/ 92 |
| mail.cooinpilot.io | 0/ 90 |
| www.cooinpilot.io | 0/ 90 |
Communicating files 0 not fetched yet
Malware samples that contacted this domain while being analysed.
Historical WHOIS · VirusTotal 1
- Registrant Organization
- REDACTED FOR PRIVACY
- Registrant Country
- US
- Name Server
- NS1.MOCK-DNS.EXAMPLE
Historical certificates 0 VT · 1 CT not fetched yet
CERTIFICATE TRANSPARENCY (crt.sh / CertSpotter) — the registrable domain and its subdomains
| Not before | Names | Issuer |
|---|---|---|
| 2026-09-01 | mail0.cooinpilot.io-cdn.net | Mock CA |
Observation timeline
- 2026-10-14 09:46:22 · HTTP 200 · state new · datacenter · content changed · 2cefb68bc475 · screenshot
- 2026-10-14 09:49:02 · HTTP 200 · state flagged · datacenter · 2cefb68bc475 · screenshot
first seen 2026-10-14 09:46 · scans 2 · next 2026-10-14 21:49 · candidate state flagged · WHOIS history →
Score history
| When | Score | Severity | Confidence | Version |
|---|---|---|---|---|
| 2026-10-14 09:46:23 | 75 | critical | 90% | v7-f1ba3ebf |
| 2026-10-14 09:49:03 current | 75 | critical | 100% | v7-f1ba3ebf |
Evidence · chain of custody ? ⚙ immutable · DB-enforced
Append-only by the database: UPDATE and DELETE are rejected by triggers, even for an admin. Every artifact is stored under its own SHA-256, so the hash is literally the file name — any tampering is visible. Role: primary = proves a signal · supporting = corroborates · contradicting = argues the site is legitimate · context = background.
| Observed (UTC) | Type | Role | Source | SHA-256 | Details | |
|---|---|---|---|---|---|---|
| 2026-10-14 09:49:03 | http · referer view | supporting | mock:playwright | 2cefb68bc475ac31 | probe: referer status: 200 content_sha256: 2cefb68bc475ac31eee337d0800… +3 | |
| 2026-10-14 09:49:03 | http · residential view | supporting | mock:playwright | 2cefb68bc475ac31 | probe: residential status: 200 content_sha256: 2cefb68bc475ac31eee337d0800… +3 | |
| 2026-10-14 09:49:03 | http · param view | supporting | mock:playwright | 2cefb68bc475ac31 | probe: param status: 200 content_sha256: 2cefb68bc475ac31eee337d0800… +3 | |
| 2026-10-14 09:49:03 | http · bot view | supporting | mock:playwright | 2cefb68bc475ac31 | probe: bot status: 200 content_sha256: 2cefb68bc475ac31eee337d0800… +3 | |
| 2026-10-14 09:49:02 | reputation | contradicting | mock:safebrowsing | — | status: negative | |
| 2026-10-14 09:49:02 | reputation | context | mock:urlhaus | — | status: unknown | |
| 2026-10-14 09:49:02 | reputation | context | mock:virustotal | — | status: unknown | |
| 2026-10-14 09:49:02 | whois | context | mock:rdap | — | status: positive | |
| 2026-10-14 09:49:02 | favicon | primary | mock:playwright | 00083f2aa3e85f30 | mmh3: 1130316202 phash: f5d52a853a95688d | artifact |
| 2026-10-14 09:49:02 | ssl | context | mock:playwright | — | fingerprint_sha256: bbbbbbbbbbbbbbbbbbbbbbbbbbb… | |
| 2026-10-14 09:49:02 | screenshot · datacenter view | primary | mock:playwright | d33cdf55b7cbb901 | phash: a8696e721b5f440f dhash: 1993b2929ab62465 palette: ['#40b384', '#5a657e', '#59… | artifact |
| 2026-10-14 09:49:02 | html · datacenter view | primary | mock:playwright | 2cefb68bc475ac31 | title: CoinPilot — Automated crypt… forms: 1 parked: False | artifact |
show all 28 evidence rows from 2 scan(s)
| 2026-10-14 09:49:02 | http | supporting | mock:playwright | 2cefb68bc475ac31 | status: 200 final_url: https://www.coinpilot.io/ content_type: text/html; charset=utf-8 | |
| 2026-10-14 09:49:02 | dns | supporting | mock:local_dns | — | status: positive | |
| 2026-10-14 09:46:23 | http · residential view | supporting | mock:playwright | 2cefb68bc475ac31 | probe: residential status: 200 content_sha256: 2cefb68bc475ac31eee337d0800… +3 | |
| 2026-10-14 09:46:22 | http · referer view | supporting | mock:playwright | 2cefb68bc475ac31 | probe: referer status: 200 content_sha256: 2cefb68bc475ac31eee337d0800… +3 | |
| 2026-10-14 09:46:22 | http · bot view | supporting | mock:playwright | 2cefb68bc475ac31 | probe: bot status: 200 content_sha256: 2cefb68bc475ac31eee337d0800… +3 | |
| 2026-10-14 09:46:22 | http · param view | supporting | mock:playwright | 2cefb68bc475ac31 | probe: param status: 200 content_sha256: 2cefb68bc475ac31eee337d0800… +3 | |
| 2026-10-14 09:46:22 | reputation | contradicting | mock:safebrowsing | — | status: negative | |
| 2026-10-14 09:46:22 | reputation | context | mock:urlhaus | — | status: unknown | |
| 2026-10-14 09:46:22 | reputation | context | mock:virustotal | — | status: unknown | |
| 2026-10-14 09:46:22 | whois | context | mock:rdap | — | status: positive | |
| 2026-10-14 09:46:22 | ssl | context | mock:playwright | — | fingerprint_sha256: bbbbbbbbbbbbbbbbbbbbbbbbbbb… | |
| 2026-10-14 09:46:22 | favicon | primary | mock:playwright | 00083f2aa3e85f30 | mmh3: 1130316202 phash: f5d52a853a95688d | artifact |
| 2026-10-14 09:46:22 | screenshot · datacenter view | primary | mock:playwright | d33cdf55b7cbb901 | phash: a8696e721b5f440f dhash: 1993b2929ab62465 palette: ['#40b384', '#5a657e', '#59… | artifact |
| 2026-10-14 09:46:22 | html · datacenter view | primary | mock:playwright | 2cefb68bc475ac31 | title: CoinPilot — Automated crypt… forms: 1 parked: False | artifact |
| 2026-10-14 09:46:22 | http | supporting | mock:playwright | 2cefb68bc475ac31 | status: 200 final_url: https://www.coinpilot.io/ content_type: text/html; charset=utf-8 | |
| 2026-10-14 09:46:22 | dns | supporting | mock:local_dns | — | status: positive |
Advisory opinions · shown for context, never part of the score ⚙ AI advisory · JSON schema
AI · mock:openai phishing impersonating CoinPilot · 65% — credential form; page presents itself as CoinPilot
classifier · ml-5edcdd68-20 P(phishing) = 74% (cross-validated accuracy 94%)